
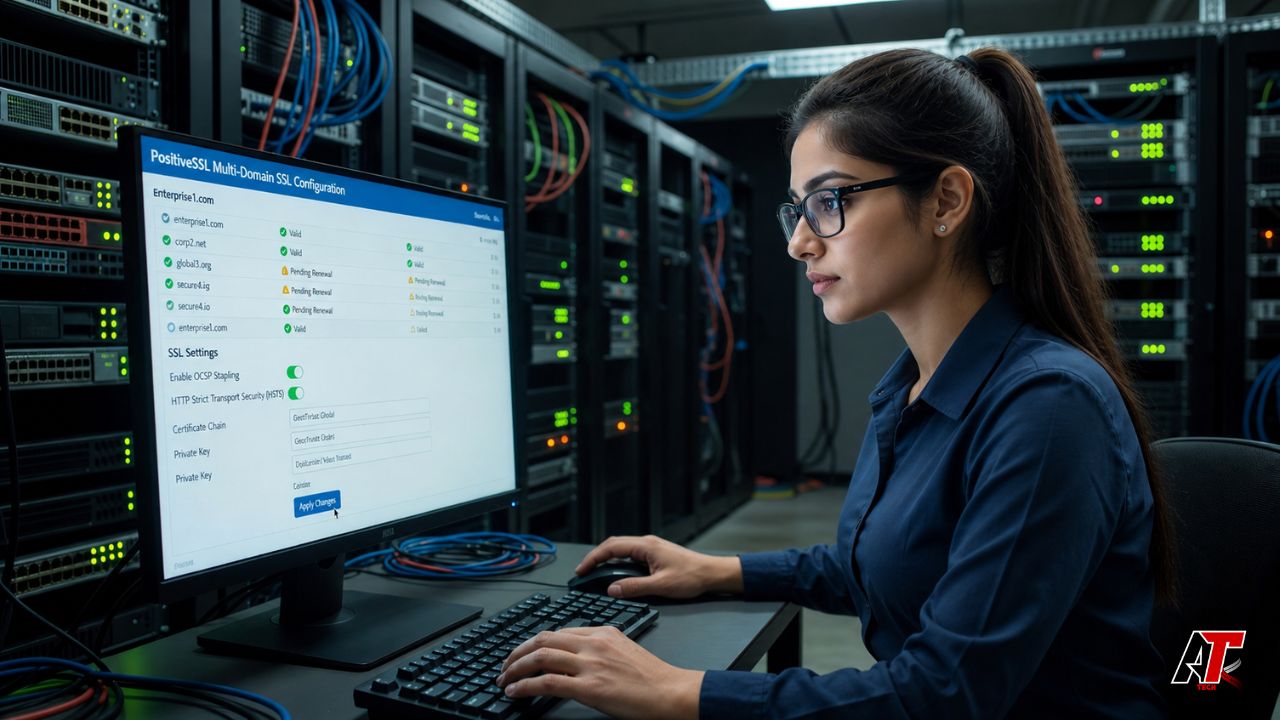
Managing secure connections across numerous web properties presents a significant challenge for IT administrators. Consolidating cryptographic security into a single, manageable framework is highly advantageous. A PositiveSSL Multi-Domain certificate provides an excellent solution by securing several distinct domains under one powerful cryptographic signature. Furthermore, this approach drastically reduces administrative overhead and total licensing costs. Therefore, organizations can scale their web infrastructure efficiently while maintaining strict security standards.
The Strategic Advantage of PositiveSSL Multi-Domain
Enterprise IT environments frequently manage multiple top-level domains for various marketing campaigns and internal applications. Purchasing individual SSL certificates for each property creates chaotic renewal schedules and inflated costs. A PositiveSSL Multi-Domain certificate consolidates this scattered infrastructure into a single trust anchor. Administrators track one expiration date instead of dozens. Consequently, the risk of accidental certificate expiration drops dramatically. Thus, consolidating domains offers both financial and operational relief for busy network teams.
Simplifying Enterprise PKI Management
Public Key Infrastructure management requires meticulous attention to detail. When administrators use a PositiveSSL Multi-Domain certificate, they generate a single Certificate Signing Request. They also manage a single private key. This centralized approach simplifies server configuration across load balancers and reverse proxies. Therefore, IT teams spend less time on routine cryptographic housekeeping. Consequently, they redirect their focus toward proactive security monitoring and system optimization.
Supporting SaaS and Cloud Architectures
Software-as-a-Service platforms often provide white-labeled portals on unique domains. Each client typically receives a custom URL. A PositiveSSL Multi-Domain certificate secures these client portals efficiently. The provider manages one certificate instead of hundreds. Consequently, the provider reduces backend complexity. Furthermore, the provider passes operational savings to clients. Thus, SaaS architectures benefit immensely from consolidated SSL deployment.
Core Features of PositiveSSL Multi-Domain
This specific certificate type offers a robust set of features tailored for cost-conscious yet security-aware organizations. It provides Domain Validation, ensuring rapid issuance without extensive corporate paperwork. Furthermore, the certificate utilizes the Subject Alternative Name extension to list multiple hostnames. Therefore, a single installation secures your primary domain, subdomains, and entirely separate base domains simultaneously. Thus, it blends convenience with powerful cryptographic protection.
High Assurance and Browser Compatibility
Despite being a Domain Validation product, it delivers high assurance through its underlying cryptographic chain. Backed by the Sectigo root certificate, it enjoys recognition across all major browsers and operating systems. Users will not encounter annoying trust warnings when navigating to secured domains. Furthermore, the certificate supports up to 256-bit encryption, ensuring data remains private during transit. Therefore, businesses project a professional, secure image to their customers. Consequently, strong browser compatibility prevents user friction and abandoned transactions.
ECC Algorithm Support for Modern Security
Modern cryptographic standards demand efficiency. This certificate supports Elliptic Curve Cryptography keys alongside traditional RSA keys. ECC keys are significantly smaller but offer equivalent or stronger security. Smaller keys reduce the computational load during the SSL handshake. Therefore, servers process connections faster. Consequently, website latency drops during high traffic events. Thus, supporting ECC algorithms modernizes the security infrastructure.
How PositiveSSL Multi-Domain Enhances Operational Efficiency
Speed is critical when deploying new web services. Traditional Organization Validation certificates can take days to process due to manual business checks. A PositiveSSL Multi-Domain certificate bypasses this bottleneck by utilizing automated Domain Control Validation. The system simply verifies that the applicant controls the listed domains. Therefore, IT teams receive their signed certificate within minutes of submitting the request. Consequently, rapid deployment cycles accelerate time-to-market for new digital initiatives.
Streamlined Issuance and Activation
The activation process requires minimal technical friction. Administrators choose a validation method, such as DNS TXT record or email verification, for each domain. Once the system confirms control, the certificate issues automatically. Furthermore, vendors often provide free reissues during the certificate lifespan. If an administrator needs to add a new domain later, they simply request a reissue. Therefore, the certificate scales alongside the business without requiring a new purchase. Thus, streamlined activation and flexible reissuance make ongoing management highly efficient.
Enabling HTTP/2 for Performance Optimization
Browsers require HTTPS to unlock HTTP/2 protocol advantages. HTTP/2 multiplexes requests over a single connection, drastically speeding up page load times. A PositiveSSL Multi-Domain certificate enables HTTPS across all listed domains. Therefore, the entire web portfolio benefits from advanced protocol features. Consequently, user experience improves and bounce rates decrease. Thus, SSL consolidation directly impacts site performance metrics.
Comparing PositiveSSL Multi-Domain to Wildcard Options
Buyers often debate between multi-domain and wildcard certificates. A wildcard certificate secures an unlimited number of subdomains under a single base domain. However, it cannot secure different top-level domains. For example, a wildcard for *.company.net cannot secure company.com. Conversely, a PositiveSSL Multi-Domain certificate secures company.net, company.com, and specific subdomains like app.company.org. Therefore, the choice depends strictly on the domain architecture. If an organization manages disparate top-level domains, multi-domain is the only viable option.
When to Choose Multi-Domain Over Wildcard
Marketing departments frequently run campaigns on unique domains to track analytics. A multi-domain certificate perfectly supports this strategy by securing all campaign URLs under one roof. Furthermore, organizations migrating from an old domain to a new one need both domains active simultaneously during the transition. A multi-domain certificate facilitates this seamless migration. Therefore, it offers unmatched flexibility for dynamic corporate environments. Consequently, combining a multi-domain certificate with wildcard entries provides the ultimate architectural freedom.
Deployment Best Practices for PositiveSSL Multi-Domain
Deploying a unified certificate requires careful planning. Because one private key secures multiple domains, administrators must protect that key rigorously. If a single server is compromised, the attacker could impersonate every domain listed on the certificate. Therefore, limiting the distribution of the private key is a critical best practice. Administrators should restrict file permissions and utilize hardware security modules where possible. Consequently, strong key management prevents catastrophic security breaches.
Securing the Private Key Across Multiple Servers
Load-balanced environments require the certificate to live on multiple servers simultaneously. To secure the key across these distributed servers, administrators must employ secure file transfer protocols. They should avoid storing private keys in plain text repositories. Furthermore, implementing Server Name Indication ensures the server presents the correct certificate for each requested domain. Therefore, proper server configuration guarantees that clients establish a secure connection without errors. Thus, meticulous deployment practices maximize the security value of the unified certificate.
SSL Termination at the Network Edge
Modern architectures rely heavily on load balancers to distribute traffic. The load balancer handles SSL termination, offloading cryptographic work from the application servers. A PositiveSSL Multi-Domain certificate installs perfectly on these edge devices. The backend servers communicate over unencrypted, high-speed channels. Therefore, the application experiences lower latency. Consequently, SSL termination centralizes security management at the network edge. Thus, load balancer integration maximizes both security and application speed.
Future-Proofing Web Architecture with PositiveSSL Multi-Domain
Digital expansion demands scalable security infrastructure. As companies acquire new brands or launch microservices, their domain count grows rapidly. A PositiveSSL Multi-Domain certificate future-proofs this expansion by allowing additional domains later. Administrators simply add the new hostnames and process a free reissue. Therefore, the security framework adapts instantly to business growth without budget overruns. Consequently, organizations maintain continuous encryption coverage during aggressive expansion phases.
Scaling Domains Without Downtime
Adding a new domain to an existing certificate does not require taking web services offline. The administrator requests the reissue, installs the new document, and reloads the web server. The transition happens in seconds. Furthermore, utilizing Automated Certificate Management Environment protocols makes this process entirely hands-off. The server software automatically detects new domains and requests the reissue. Therefore, human error never disrupts the secure connection. Thus, seamless scaling ensures high availability and persistent trust for expanding enterprises.
FAQs
1. What is a PositiveSSL Multi-Domain certificate?
It is a domain-validated SSL certificate that secures multiple distinct domain names under a single cryptographic signature.
2. How many domains can I secure with one certificate?
The base license typically secures three domains, but you can purchase additional Subject Alternative Name slots as needed.
3. Does this certificate require business documentation?
No, it uses Domain Control Validation, so it only requires you to prove control over the listed domains for rapid issuance.
4. Can I secure subdomains with this certificate?
Yes, you can list specific subdomains as Subject Alternative Names on the certificate during the request process.
5. Can I add new domains after purchasing the certificate?
Yes, vendors offer unlimited free reissues, allowing you to add or remove domains anytime during the lifecycle.
6. Is this certificate recognized by all web browsers?
Yes, it is backed by a highly trusted root certificate, ensuring compatibility with all major browsers and mobile devices.
Conclusion
Consolidating cryptographic security across multiple web properties is a strategic necessity for modern enterprises. A PositiveSSL Multi-Domain certificate offers an excellent, powerful solution by securing disparate domains under a single administrative umbrella. This approach drastically reduces licensing costs and simplifies lifecycle management while providing robust 256-bit encryption. By leveraging rapid Domain Validation and free reissues, IT teams can scale their infrastructure dynamically without friction. Ultimately, deploying this unified SSL solution empowers organizations to maintain high security and browser trust while optimizing their operational efficiency.
Leave a Reply